When a production pipeline fails, someone needs elevated access, fast. We grant it. The pipeline recovers. Everyone goes back to bed. But what happens to the access?
That’s where privileged access management earns its keep. For the security operations center (SOC), the useful questions are straightforward: who received access, why, what happened, and can we prove it ended?
What is PAM?
Privileged access management (PAM) combines policies, processes, and technologies to control and audit elevated access to systems and data. It governs sensitive capabilities, including changing security settings, administering databases, and granting other identities access.
The principle of least privilege establishes the goal: only the permissions necessary for the task. PAM helps enforce that goal wherever elevated access is involved.
Constellation Research’s 2026 PAM overview identifies credential protection, session monitoring, temporary elevation, strong authentication, and least-privilege enforcement as core capabilities.
A password vault is part of that toolkit. It isn’t the entire program.
What counts as privileged access?
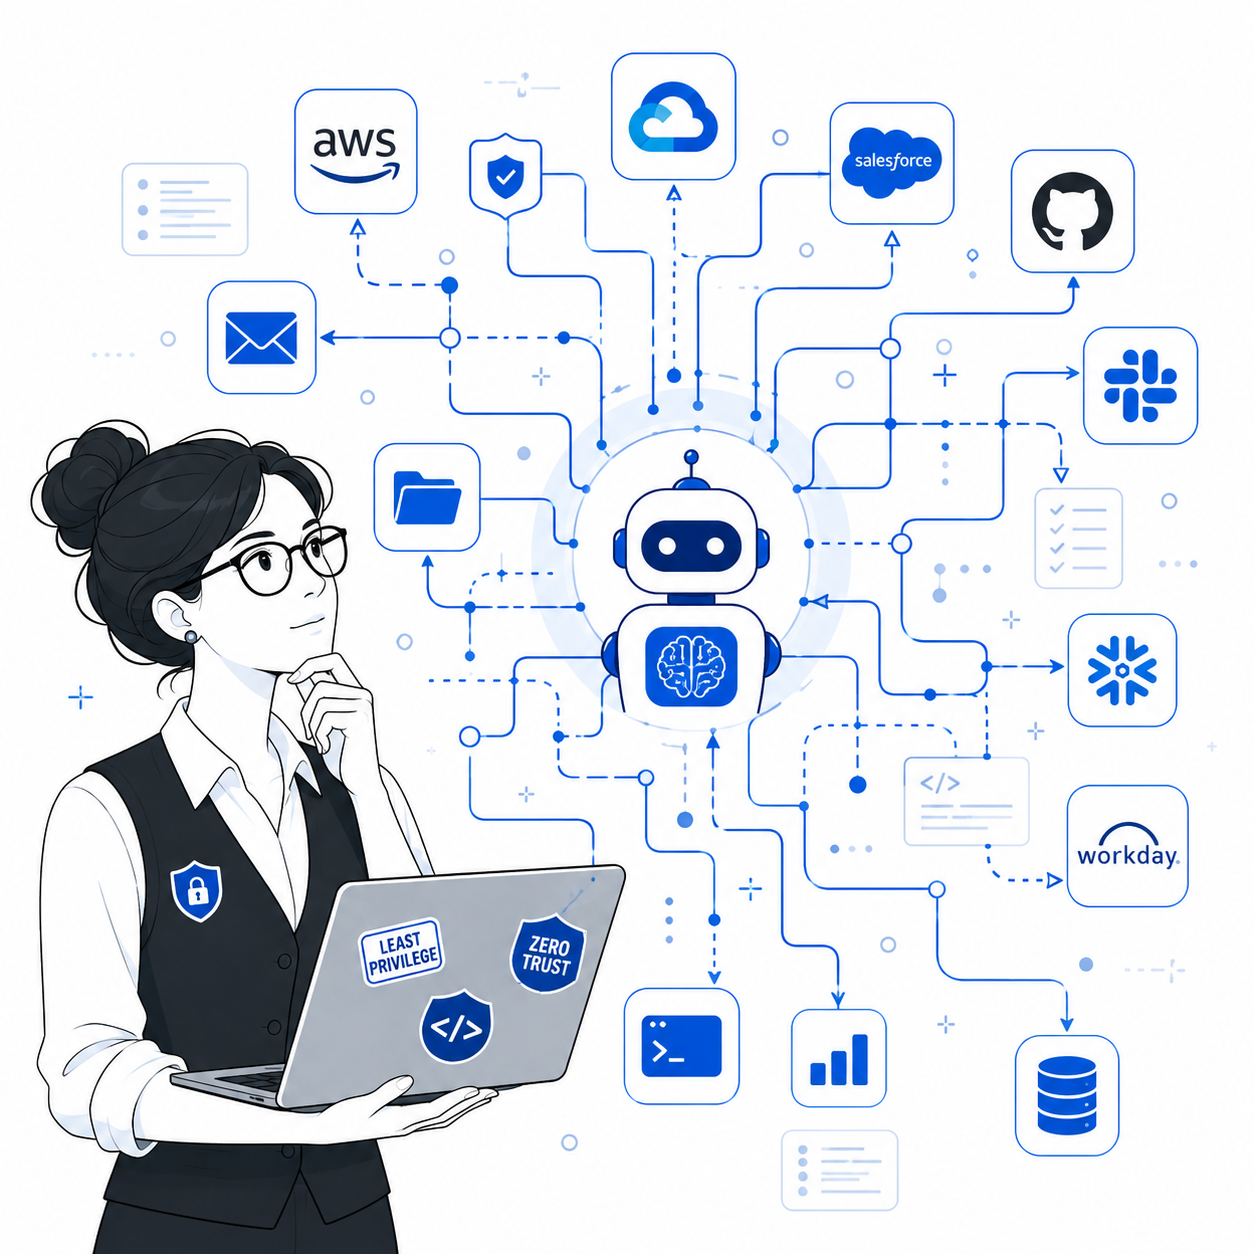
Administrator accounts are the obvious candidates. Cloud roles, deployment pipelines, service accounts, and artificial intelligence (AI) agents also deserve attention.
Privilege depends on what an identity can do. A workload with broad permissions may change production infrastructure without ever opening an administrator console. Conveniently, attackers don’t require a job title.
KuppingerCole’s May 2026 PAM analysis describes privilege across human identities, automated workloads, cloud policies, and emerging agents.
That makes service account security part of the conversation. Machine access needs an owner, a purpose, appropriate permissions, and a managed credential lifecycle.
Sensitive data access also warrants scrutiny, even when it doesn’t confer administrative control.
How does PAM work?
A practical lifecycle is:
Discover → assess → authorize → grant → observe → revoke → review.
We identify elevated permissions, establish who needs them, apply authentication and approval policies, grant scoped access, and record its use. Afterward, we remove access and check the outcome.
Credential vaulting and rotation protect reusable secrets. Session monitoring helps reconstruct interactive activity. Cloud and application logs provide evidence for actions that never pass through a recorded terminal.
Implementation varies. We should verify coverage against actual workflows rather than assuming one product sees everything.
PAM vs. IAM: where the controls fit
Identity and access management (IAM) governs access broadly. PAM concentrates on elevated access.
Privileged identity management (PIM) addresses privileged identities or role assignments, although terminology varies by platform. Cloud infrastructure entitlement management (CIEM) examines cloud permissions and excessive entitlements. Identity threat detection and response (ITDR) focuses on detecting and containing identity attacks.
These functions overlap. The integration matters more than winning acronym bingo.
Just-in-time access isn’t automatically zero standing privilege
Just-in-time (JIT) access limits when elevated access is available. Least privilege limits its scope.
The goal of zero standing privileges is to eliminate persistent privileged permissions within the environment we’re addressing.
Temporarily checking out a permanently powerful account doesn’t automatically remove its underlying privilege. KuppingerCole’s July 2026 analysis makes that distinction explicitly: zero standing privilege is an operating model, supported by several controls.
We need to examine what remains available between approved tasks.
PAM for the SOC: follow one production incident
Return to our failed pipeline.
In a controlled workflow, the on-call engineer requests a maintenance role for 30 minutes, linked to the incident. Policy checks eligibility, requires approval where appropriate, and restricts the grant to the affected resources.
Access automation handles the repeatable steps. The engineer repairs the pipeline. Relevant activity reaches the investigation workflow.
Now suppose that identity attempts an unrelated permission change.
We need to connect the actor, approved task, effective permissions, timestamps, and observed action. Identity provenance helps explain where the permission originated and which decision authorized it.
The SOC can then investigate and coordinate containment with the system owner. An approval proves access was authorized; it doesn’t prove every subsequent action was legitimate.
Expiration needs evidence
A grant expiring doesn’t necessarily terminate every active session or invalidate every issued token. Behavior depends on the platform and enforcement mechanism.
- The National Institute of Standards and Technology’s September 2026 token protection guidance addresses token security and revocation. For our playbooks, the implication is practical: test what remains usable after access is withdrawn.
Effective deprovisioning needs confirmation at the target system. “Request completed” is reassuring. “Access denied” is evidence.
We also need tested break-glass procedures when normal access infrastructure fails, with monitoring, accountable ownership, and retrospective review.
Start small, measure what changes
Begin with one high-impact production environment. Find privileged identities, remove unnecessary permissions, investigate orphaned accounts, and pilot temporary elevation.
Measure standing privileged assignments, successful access expiration, time to confirmed revocation, and legitimate request turnaround. Security that routinely obstructs recovery invites workarounds.
Keep ownership explicit: resource owners define appropriate access, identity teams operate controls, and responders follow agreed containment authority.
The acceptance test is easy: can we identify the actor, explain the grant, reconstruct the activity, and prove access ended? If we can’t, the ticket may be closed. The exposure isn’t.
Starting PAM today
Ready to stop temporary access becoming permanent baggage? Get the Trustle free trial to discover excessive cloud permissions and test time-limited access with automated expiration across supported integrations. Let’s give elevated access a purpose, and an end time.